
Implementing NIST CSF 2.0 step by step gives CTOs a no-nonsense way to move from scattered security efforts to a focused, risk-driven program. You map where you are today, decide where you need to be, close the gaps, and keep improving—without getting lost in paperwork or vendor hype.
If you’re still figuring out the bigger picture, jump back to our guide on Cybersecurity frameworks for CTO implementation for the full context on why this framework fits most U.S. organizations.
Here’s the quick overview:
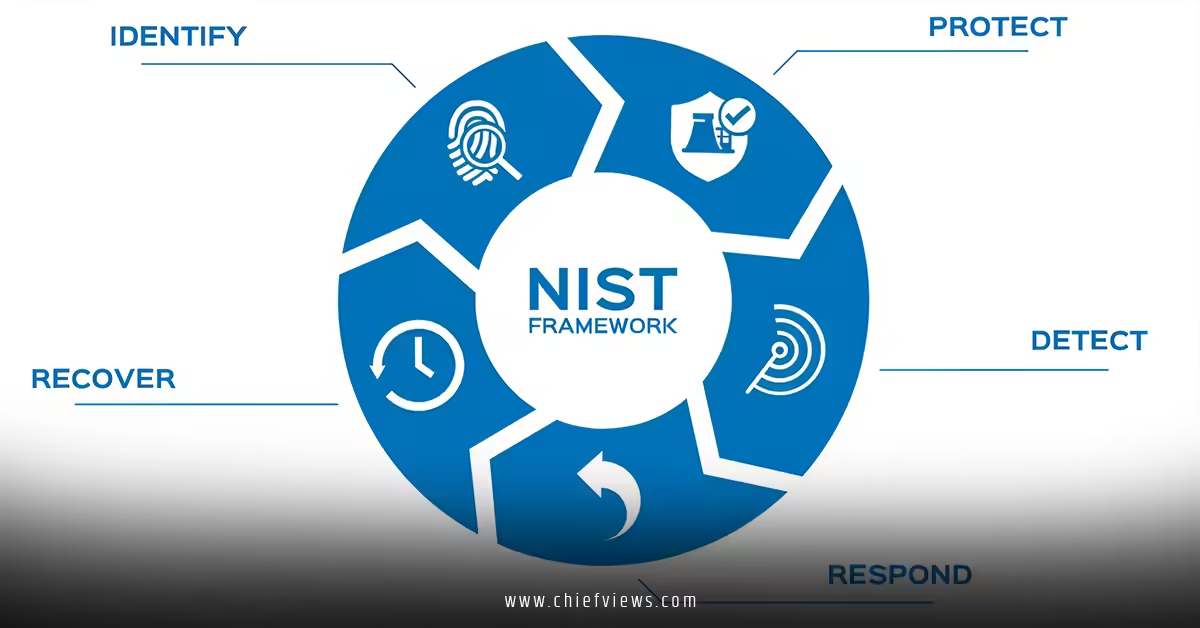
- Six core functions—Govern, Identify, Protect, Detect, Respond, Recover—form the backbone.
- Profiles turn theory into your reality: one for today’s state, one for your target.
- Iterative process means you don’t do it once and forget it.
- Works for any size—SMBs use the free Small Business Quick-Start Guide; enterprises layer in enterprise risk management.
- 2026-ready with fresh Quick-Start Guides on workforce integration and informative references.
Why NIST CSF 2.0 Still Dominates in 2026
Threats keep evolving—AI-driven attacks, tighter supply-chain rules, board-level scrutiny. NIST CSF 2.0 stays voluntary, flexible, and free. The “Govern” function added in 2.0 forces leadership accountability right from the start. No more security as an IT silo.
In my experience, CTOs who follow the steps see three immediate wins: clearer board conversations, defensible budget asks, and measurable risk reduction within the first year.
Think of it like building a house. You don’t slap on drywall before the foundation and framing are solid. CSF 2.0 is your blueprint—everything else (tools, training, audits) snaps into place.
The Six Functions at a Glance
| Function | What It Covers | Real-World CTO Payoff |
|---|---|---|
| Govern | Leadership, policy, risk strategy | Board-ready oversight and accountability |
| Identify | Assets, risks, business context | You know exactly what’s worth protecting |
| Protect | Safeguards, access control, training | Day-to-day defenses that actually work |
| Detect | Monitoring, anomalies, alerts | Catch trouble before it becomes a crisis |
| Respond | Incident plans, communication, analysis | Faster, calmer reaction when it hits |
| Recover | Restoration, lessons learned, resilience | Bounce back stronger and faster |
These aren’t checkboxes. They overlap on purpose—Govern runs through everything.
Implementing NIST CSF 2.0 Step by Step: The 7-Step Roadmap
Follow this exact sequence. It’s pulled straight from NIST guidance and proven in the trenches.
1. Prioritize and Scope
Decide what’s in bounds. Critical systems? Customer data? Cloud workloads? Get your executive team in a room and ask one question: “What would actually hurt the business if it went down?” Document that scope. Short answer: Don’t boil the ocean on day one.
2. Orient the Organization
Build context. Review regulations (HIPAA, CMMC, SEC rules), supply-chain contracts, and current tools. Pull in stakeholders from legal, HR, and operations. This step stops you from implementing controls in a vacuum.
Grab the latest NIST Quick-Start Guides here: nist.gov/cyberframework/quick-start-guides.
3. Create a Current Profile
List every relevant outcome from the CSF Core and mark where you stand today. Use the free Excel template from NIST or a simple spreadsheet. Be brutally honest—most teams discover they’re weaker in Detect and Recover than they thought.
4. Conduct a Risk Assessment
Score threats by likelihood and impact. Factor in 2026 realities: AI prompt injection, third-party breaches, ransomware-as-a-service. Use your own data or reference NIST SP 800-30 for methodology. Output: a prioritized risk register.
5. Create a Target Profile
Decide your desired state for each outcome. Tier 1 (partial) to Tier 4 (adaptive)—pick what matches your risk appetite. For most mid-market companies, Tier 3 is realistic within 18 months.
6. Analyze and Prioritize Gaps
Compare Current vs. Target. Rank gaps by risk reduction per dollar and effort. Quick wins first: MFA everywhere, asset inventory, backup testing. Big projects (zero-trust rollout) get phased in.
7. Implement the Action Plan
Assign owners, deadlines, and success metrics. Integrate into existing OKRs. Test, train, and measure. Then loop back—CSF 2.0 is a cycle, not a project. Review every quarter.
New in 2026: Check NIST SP 1308 for tying cybersecurity into enterprise risk management and workforce planning. It makes the “Govern” function actually useful instead of theoretical.
Common Mistakes When Implementing NIST CSF 2.0 (and Quick Fixes)
- Treating profiles as one-and-done → Fix: Schedule annual refreshes tied to business planning.
- Skipping the Govern function → Fix: Start every steering meeting with risk-tolerance questions from leadership.
- Over-documenting early → Fix: Use the Small Business Quick-Start Guide (NIST SP 1300) if you’re under 500 employees.
- Ignoring people and process → Fix: Build training into Protect and run tabletop exercises in Respond.
- No metrics → Fix: Track mean-time-to-detect, patch compliance, and recovery time—report them upward.
- Trying to hit Tier 4 immediately → Fix: Aim for steady progress. Momentum beats perfection.
Key Takeaways
- Implementing NIST CSF 2.0 step by step is the fastest way for CTOs to turn security from a cost center into a business enabler.
- Start with scope and Govern—everything else flows from there.
- Profiles are your secret weapon: current + target = crystal-clear roadmap.
- Use the free NIST resources; they’re updated for 2026 realities.
- Make it iterative—quarterly reviews keep you ahead of threats.
- Combine with other frameworks if customers demand ISO or SOC 2.
- Measure outcomes, not just activities.
- Leadership buy-in isn’t optional—it’s the new table stakes.
Next step: Download the Organizational Profile template from nist.gov today and schedule a two-hour scoping workshop with your leadership team this month. Small move, massive payoff.
FAQs
How long does implementing NIST CSF 2.0 step by step usually take?
Most organizations see meaningful progress in 6–12 months and full maturity in 18–24 months. It depends on starting point and team size—SMBs move faster with the dedicated Quick-Start Guide.
Is NIST CSF 2.0 mandatory for U.S. companies?
No. It’s voluntary guidance. That said, many regulators and customers treat it as the de-facto standard, especially in critical infrastructure and federal contracting.
Do I need special tools to implement NIST CSF 2.0?
Not at first. A spreadsheet works fine. Later you can layer GRC platforms or automation for continuous monitoring.
How does the new 2026 Quick-Start Guide change implementation?
SP 1308 shows you how to weave cybersecurity risk into enterprise risk management and workforce decisions—making “Govern” far more practical for CTOs reporting to the board.
Can small teams implement NIST CSF 2.0 without consultants?
Absolutely. Start with NIST SP 1300 Small Business Quick-Start Guide and the Implementation Examples. Bring in help only for the risk assessment or gap analysis if internal bandwidth is tight.