
A cyber risk quantification framework turns technical vulnerabilities and threat scenarios into financial numbers decision-makers can use. Instead of “high” or “critical,” you get expected annual loss ranges, probability distributions, and clear trade-offs between spending on controls and accepting residual exposure.
Organizations that adopt a structured cyber risk quantification framework stop arguing about severity scores and start allocating capital the same way they manage every other material risk. The shift is practical, not theoretical.
Why a Cyber Risk Quantification Framework Matters in 2026
Boards and CFOs no longer accept heat maps. They want numbers that sit alongside credit risk, market risk, and operational risk. Regulatory expectations, especially SEC disclosure rules and growing cyber insurance scrutiny, push the same direction.
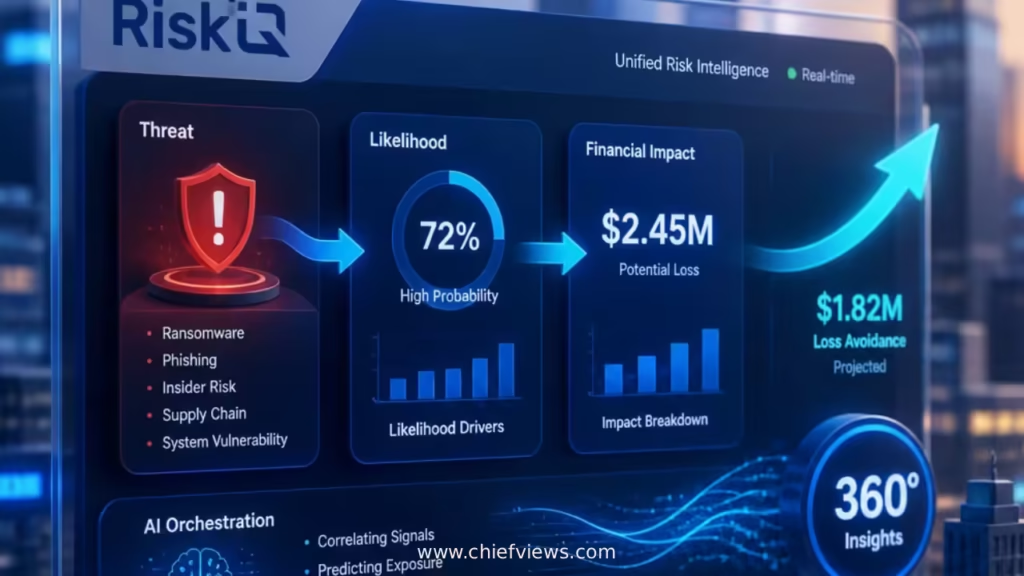
Without a framework, security teams present lists of findings. With one, they present scenarios such as: “There is a 10–18 % chance this year of a ransomware event costing $2.8–9.4 million.” That language drives budget decisions, insurance negotiations, and prioritization.
This approach builds directly on Translating Cyber Risk into Financial Exposure by giving teams the repeatable process that makes the translation consistent and defensible.
Core Components of an Effective Cyber Risk Quantification Framework
Most mature programs rest on a few shared elements:
1. Scenario definition
Start with specific, high-consequence scenarios rather than abstract risks. Examples: ransomware on revenue-critical systems, third-party breach exposing customer records, or business email compromise leading to fraud. Vague scenarios produce vague numbers.
2. Frequency estimation
How often is the event expected to occur? Pull from internal incident history, threat intelligence, control effectiveness data, and industry benchmarks. Express the result as a range (for example, 0.07–0.21 events per year).
3. Magnitude estimation
What does it cost when the event happens? Break losses into primary (incident response, recovery, downtime) and secondary (regulatory fines, notification, customer attrition, legal exposure). Use your own downtime cost per hour and customer lifetime value where possible.
4. Aggregation and simulation
Multiply frequency by magnitude, then apply Monte Carlo simulation or similar techniques to generate a loss distribution. Output expected annual loss plus confidence intervals. The range is more useful than a single point estimate.
5. Decision mapping
Tie every quantified scenario to a business decision: invest in a control, buy more insurance, accept the residual risk, or transfer it. Quantification without action is just expensive reporting.
Leading Frameworks in Practice
FAIR (Factor Analysis of Information Risk) remains the most widely adopted open standard. It decomposes risk into Loss Event Frequency and Loss Magnitude, then further into measurable sub-factors. The FAIR Institute maintains training, taxonomy, and community resources. Many teams begin with a spreadsheet implementation of FAIR before moving to dedicated platforms.
NIST SP 800-30 provides the process structure many U.S. organizations already use. Pair it with FAIR-style financial modeling and you gain both regulatory familiarity and dollar outputs.
Other approaches exist—actuarial models used by insurers, Bayesian networks, and proprietary vendor platforms—but the core logic stays the same: frequency × magnitude, expressed as a probability-weighted financial range.
Building Your Cyber Risk Quantification Framework: Practical Steps
- Select three to five priority scenarios. Choose those that would materially affect revenue, operations, or regulatory standing.
- Gather existing data. Vulnerability scans, incident logs, control assessments, recovery time objectives, and downtime cost estimates. Perfect data is rare; calibrated ranges based on the best available information still outperform qualitative labels.
- Estimate frequency and magnitude separately. Document assumptions and confidence levels for each input.
- Run the calculation. Even basic Excel tools or free Monte Carlo simulators produce usable distributions.
- Present results in financial language. Show the expected annual loss, the 90th-percentile loss, and the cost of the control that would reduce exposure.
- Refresh quarterly. Threats, controls, and business context change. Treat the model as living, not a one-time project.
- Link quantification to governance. Feed results into risk appetite statements, board reporting, and capital allocation processes.
Start with one scenario that matters to a business owner. Success on the first model creates demand for the rest.
Common Pitfalls and How to Avoid Them
- Chasing false precision. Ranges with stated confidence levels are more credible than single-point forecasts.
- Importing industry averages without adjustment. The U.S. average breach cost provides context, not a substitute for your own recovery costs and customer concentration.
- Treating the framework as a security project. Involve finance early so the outputs map to decisions they already make.
- Ignoring secondary losses. Regulatory, legal, and reputational costs often dominate the total.
- Failing to document assumptions. Transparency is what keeps the model defensible when challenged six months later.
How a Cyber Risk Quantification Framework Changes Decisions
Once risk is expressed in dollars, prioritization becomes clearer. A control that costs $350,000 annually and reduces expected loss by $1.6 million is an easy investment case. A tool that costs the same but only trims $120,000 of exposure faces harder scrutiny.
The same numbers improve cyber insurance discussions. Underwriters respond better to quantified residual risk than to control checklists. Boards gain a consistent way to compare cyber exposure with other enterprise risks. Security stops being a pure cost center and becomes a risk-reduction function measured in the same language as the rest of the business.
Getting Started This Quarter
Pick one high-impact scenario. Build the frequency and magnitude estimates with the data you already have. Produce a simple loss range. Present it to the relevant business owner and the finance team. Ask whether the exposure sits inside current risk appetite. That single conversation usually reveals whether the organization is ready for a broader cyber risk quantification framework.
The organizations that treat quantification as a decision-support capability—not a reporting exercise—see the fastest return. They spend less time debating severity scores and more time reducing the exposures that actually threaten the balance sheet.
Key Takeaways
- A cyber risk quantification framework converts technical threats into probability-weighted dollar ranges that finance and boards can act on.
- FAIR remains the most practical open standard; NIST SP 800-30 provides process structure many U.S. teams already use.
- Start with three to five high-consequence scenarios rather than trying to quantify everything at once.
- Use calibrated ranges and stated confidence levels—false precision destroys credibility faster than imperfect data.
- Frequency and magnitude must be estimated separately, then combined through simulation to produce expected annual loss.
- Refresh priority scenarios at least quarterly so the model stays current with threats and controls.
- Quantification only creates value when it drives real decisions: control investment, insurance limits, or risk acceptance.
- Document every assumption. Transparency is what keeps the numbers defensible under scrutiny.
FAQs
What is the difference between a cyber risk quantification framework and a traditional risk register?
A traditional risk register usually ranks items as high, medium, or low. A cyber risk quantification framework expresses those same risks as expected financial loss ranges so leaders can compare cyber exposure directly with other business risks.
Do I need expensive software to implement a cyber risk quantification framework?
No. Many teams begin with structured spreadsheets and basic Monte Carlo tools. Dedicated platforms become useful once the process is established and you want to automate data feeds, but they are not required to start.
How does a cyber risk quantification framework support Translating Cyber Risk into Financial Exposure?
The framework supplies the repeatable method—scenario definition, frequency and magnitude estimation, and simulation—that turns the concept of financial translation into consistent, defensible numbers the organization can use for decisions.

