
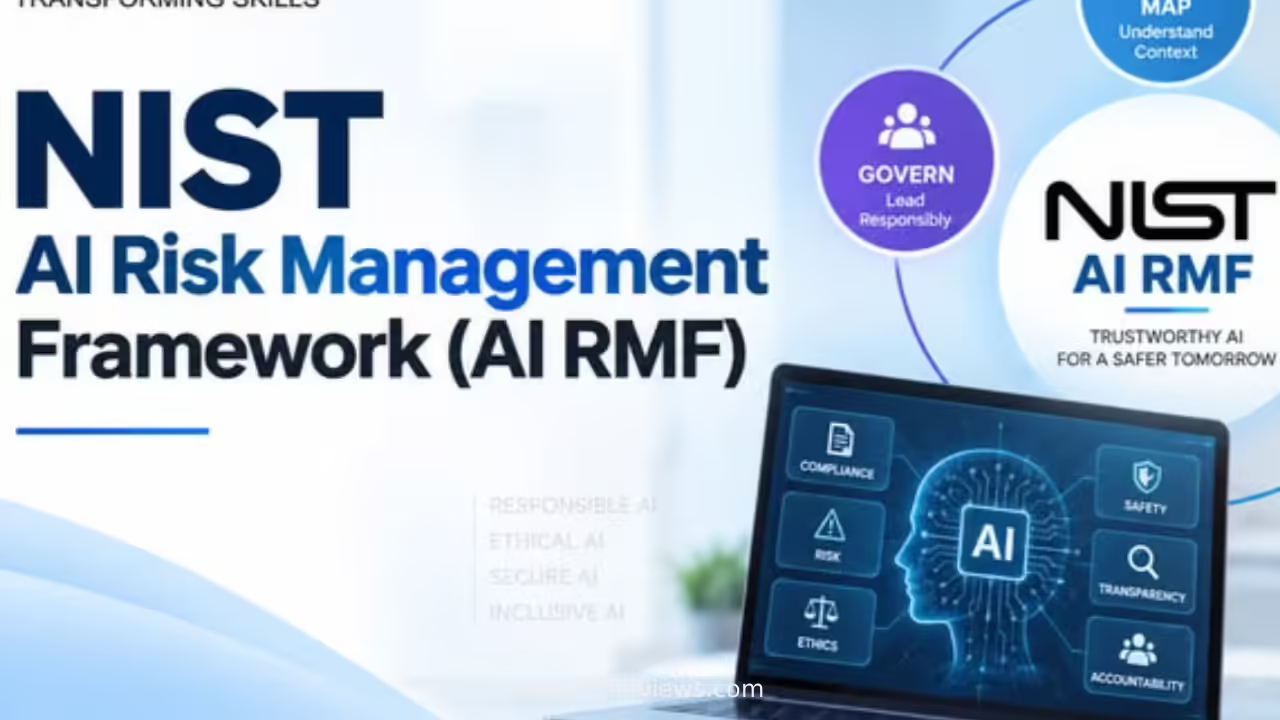
NIST AI Risk Management Framework guide is the practical playbook U.S. organizations use to turn abstract AI risk talk into repeatable actions that keep systems trustworthy and operations running.
Here’s the quick overview:
- The NIST AI RMF is a voluntary, flexible framework released in 2023 (still the current published version in 2026 while a revision is underway).
- It organizes work into four core functions: Govern, Map, Measure, and Manage.
- Companion tools include the official Playbook and the Generative AI Profile (NIST AI 600-1).
- It forms the backbone for digital resilience and compliance with AI regulations across state laws and federal expectations.
- Teams that treat it as an operating system rather than a one-time document cut both risk exposure and audit friction.
Most companies download the PDF, skim the four functions, then file it. That approach wastes the real value. The framework works when you treat the functions as a continuous loop that feeds your resilience program and satisfies the growing list of state AI rules.
Why the NIST AI Risk Management Framework Guide Matters in 2026
No comprehensive federal AI statute exists. State laws keep stacking up—Texas TRAIGA, California frontier rules, Colorado automated-decision requirements—and many of them reference or reward alignment with the NIST AI RMF. Texas even offers an affirmative defense for organizations that can show substantial compliance with the framework or its Generative AI Profile.
Federal agencies still point to it. Executive actions continue to lean on NIST standards for cybersecurity and frontier-model handling. The result is simple: if you build once to the NIST AI Risk Management Framework guide, you cover a large slice of the real compliance surface while hardening the systems that keep the business online.
In my experience, the organizations that succeed treat the RMF as the shared language between security, legal, product, and operations. Everyone stops arguing about definitions and starts tracking the same outcomes.
The Four Core Functions Explained Without the Jargon
Govern sets the culture, policies, and accountability. Who owns AI risk? How are decisions escalated? What training does the workforce get? This function runs across the entire lifecycle.
Map forces you to understand context. What is the system supposed to do? Who is affected? What data does it use? What third-party components sit inside it? You cannot manage what you have not mapped.
Measure is where testing and metrics live. You select methods, run evaluations, check for drift, bias, security weaknesses, and performance under stress. Measurement is continuous, not a launch-day checkbox.
Manage turns findings into action. You prioritize risks, decide treatments, allocate resources, and prepare response plans for when something goes wrong.
The official resources live on the NIST AI Risk Management Framework page. The companion Playbook translates each subcategory into suggested actions and documentation practices—available at the NIST AI RMF Playbook.
For generative systems, the Generative AI Profile (NIST AI 600-1) adds twelve specific risk categories and more than two hundred suggested actions.
A critical-infrastructure profile concept note appeared in April 2026, signaling further sector-specific guidance is coming.
Step-by-Step Action Plan Using the NIST AI Risk Management Framework Guide
Here’s the sequence I run with teams that need results in 90 days without drowning in process.
- Inventory and assign ownership (Days 1–14)
List every AI system—internal models, vendor tools, agentic systems, shadow AI. Name a business owner and a technical owner for each. Map the inventory to the Govern function first. - Complete the Map function for high-impact systems (Days 15–30)
Document intended use, stakeholders, data sources, third-party dependencies, and potential impacts. Rank systems by consequence (hiring, credit, healthcare, critical operations). - Select and run Measure activities (Days 31–60)
Choose testing methods that match the risk tier. Run baseline evaluations for performance, security, and fairness where relevant. Set up continuous monitoring for drift and anomalous outputs. - Decide treatments and close the Manage loop (Days 61–75)
Prioritize findings. Implement human-in-the-loop controls, fallback procedures, and incident response playbooks. Document residual risk acceptance at the right level. - Stand up the operating rhythm (Days 76–90 and ongoing)
Create a simple dashboard that tracks inventory completeness, last measurement date, open findings, and policy updates. Review quarterly or after any material model change.
NIST AI Risk Management Framework guide This sequence directly supports digital resilience and compliance with AI regulations by giving you both the technical controls and the audit trail regulators and customers expect.
Common Mistakes & How to Fix Them
Mistake one: treating the framework as a compliance checklist. The subcategories are outcomes, not tasks. Fix: start with the highest-risk systems and apply only the relevant actions from the Playbook.
Mistake two: mapping once and never updating. Context changes when models retrain or use cases expand. Fix: trigger a fresh Map cycle on every significant change and at least annually.
Mistake three: measuring only accuracy. Security, robustness under attack, and human-AI interaction matter just as much. Fix: include adversarial testing and failure-mode analysis in your Measure plan.
Mistake four: leaving Govern to the legal team alone. Culture and accountability fail when only lawyers own the policies. Fix: make the CISO or Chief AI Officer the operational owner with legal as a partner.
Mistake five: ignoring profiles. The Generative AI Profile and emerging critical-infrastructure guidance exist for a reason. Fix: apply the relevant profile on top of the core functions when the technology or sector matches.
Function Comparison Table
| Function | Primary Goal | Key Artifacts You Produce | Typical First Action | Common Failure Mode |
|---|---|---|---|---|
| Govern | Culture, policy, accountability | AI policy, roles matrix, training records | Assign named owners for every system | Policies exist but no one follows them |
| Map | Context and impact understanding | System cards, impact assessments | Complete inventory of all AI systems | Incomplete third-party visibility |
| Measure | Evidence of risk and performance | Test reports, monitoring dashboards | Baseline evaluation of high-risk systems | Metrics that never trigger action |
| Manage | Risk treatment and response | Risk register, playbooks, residual risk | Prioritize top findings and assign owners | Findings sit open indefinitely |
The table shows why the functions must run together. Strong Map work without Measure is guesswork. Solid Measure without Manage is theater.
Making the Framework Stick
The NIST AI Risk Management Framework guide delivers the most value when it becomes the shared operating language. Security teams use the Measure and Manage language. Product teams live in Map. Leadership owns Govern. Everyone points to the same outcomes.
When a new state law appears or a customer asks for evidence, you already have the structure. When a model fails in production, the response playbook is already written. That is digital resilience and compliance with AI regulations in practice—not a separate project, but the same continuous loop.
One analogy that holds up: the RMF is less like a building code you follow once and more like the standard operating procedures a commercial flight crew uses every day. Checklists, clear roles, continuous monitoring, and practiced responses keep the plane flying even when systems degrade.
Key Takeaways
- The NIST AI RMF remains voluntary but is the de-facto U.S. standard referenced by states and agencies in 2026.
- Four functions—Govern, Map, Measure, Manage—create a full risk-management loop.
- The official Playbook turns outcomes into concrete suggested actions and documentation.
- The Generative AI Profile adds targeted risks and actions for large language models and similar systems.
- Start with inventory and high-impact systems; expand from there.
- Continuous measurement and clear ownership beat one-time documentation.
- Alignment with the framework strengthens both operational resilience and regulatory readiness.
- Assign a single cross-functional owner so the work does not fragment across silos.
The teams that treat the NIST AI Risk Management Framework guide as a living operating system move faster, fail safer, and answer auditors with evidence instead of explanations. Pull the current inventory this week and run the first Map cycle on your highest-impact system. Everything else builds from there.
FAQs
Is the NIST AI Risk Management Framework guide mandatory under U.S. law?
No. It is voluntary. However, several state laws reference it for safe-harbor or affirmative-defense purposes, and federal agencies continue to use it as the primary technical standard.
How does the Generative AI Profile fit with the core NIST AI Risk Management Framework guide?
The profile is a companion resource. It maps twelve generative-AI-specific risks to the same four functions and supplies additional suggested actions. Use it on top of the core framework when generative systems are in scope.
Can small organizations realistically implement the NIST AI Risk Management Framework guide?
Yes. Focus on the highest-risk systems first, borrow only the relevant Playbook actions, and scale documentation to match organizational size. The framework is deliberately flexible for organizations of any scale.

