
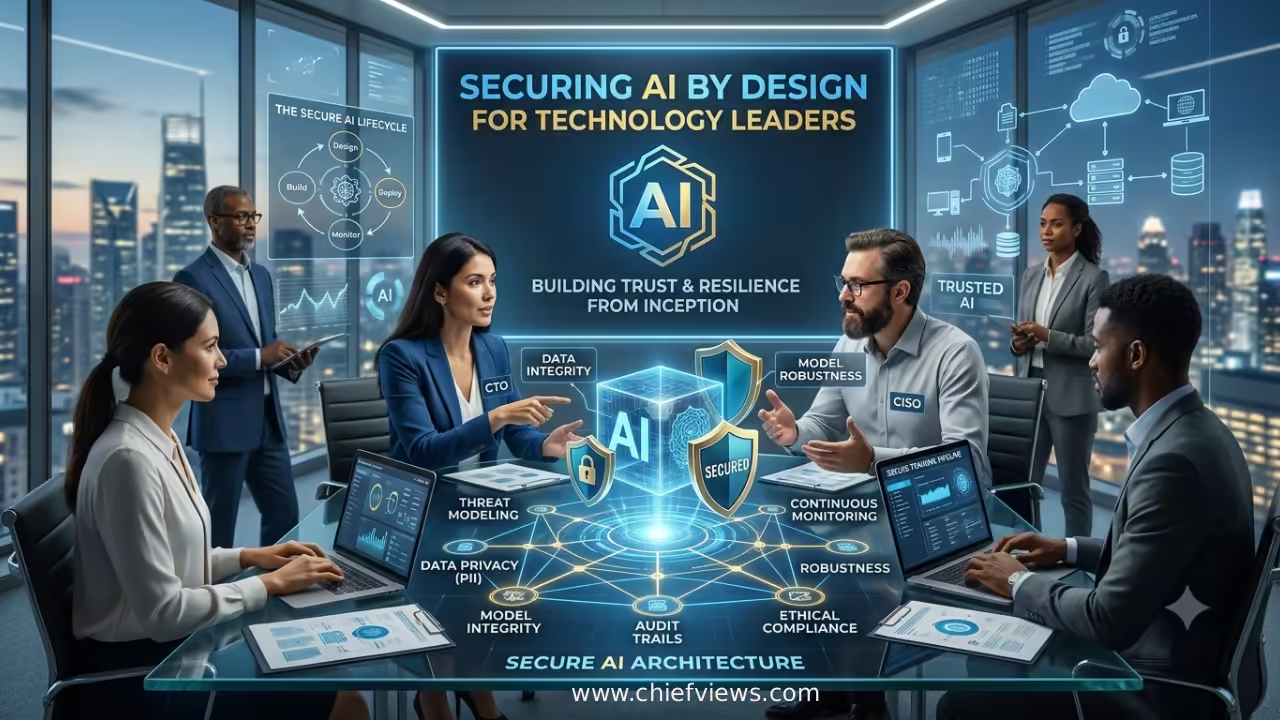
Securing AI by design for technology leaders starts with treating every model, agent, and data pipeline as an untrusted insider from day one. Bolt-on security fails here. The systems that survive 2026 threats are the ones engineered with hard boundaries, least privilege, and continuous verification baked into the architecture itself.
Quick overview for technology leaders:
- Securing AI by design means embedding controls into the full lifecycle—data, training, deployment, and runtime—rather than layering them on later.
- It treats models and agents as potential adversaries, limiting their tools, context, and authority by default.
- The approach draws from zero-trust principles, deterministic policy enforcement, and frameworks such as the NIST AI Risk Management Framework.
- Technology leaders who get this right reduce material risk while still shipping AI capabilities at speed.
- Skip it, and shadow agents, prompt injection, and data leakage become expensive facts of life.
Why Traditional Security Falls Short on AI Systems
Securing AI by design for technology leaders Most enterprise security stacks were built for deterministic software. AI systems are probabilistic, tool-using, and increasingly autonomous. An agent can chain actions across APIs, pull external data, and modify state faster than any human can review.
What usually happens is that teams deploy a promising pilot, then scramble to add guardrails after the first incident. By then the attack surface has already expanded. Prompt injection, data poisoning, model extraction, and unauthorized tool use are not edge cases—they are the new baseline.
In my experience working with CTOs and CISOs, the organizations that stay ahead treat the language model itself as untrusted. External inputs are assumed malicious. Irreversible actions require human approval or deterministic policy gates. That mindset shift is the real starting point for securing AI by design for technology leaders.
Core Principles of Securing AI by Design for Technology Leaders
Securing AI by design for technology leaders Four principles keep showing up in successful programs:
- Security goals are set before the first line of architecture is drawn.
- The system is designed under the assumption it will be attacked.
- Trusted computing base and attack surface stay minimal—agents receive only the tools and context they need for the specific task.
- Policy enforcement stays deterministic. Models propose; code decides.
These map cleanly to CISA’s broader secure-by-design guidance and to NIST’s emerging work on agent identity management. The National Institute of Standards and Technology has outlined design tenets that call for distinct, cryptographically verifiable agent identities, short-lived privileges, and continuous monitoring independent of the agent itself.
Securing AI by Design for Technology Leaders: Practical Action Plan
Here is the sequence I recommend when a technology leader wants to move from aspiration to operating reality.
Step 1: Inventory every AI asset.
Map models, agents, datasets, vector stores, and third-party tools. Include shadow AI. You cannot secure what you cannot see.
Step 2: Assign ownership and risk tiers.
Every agent needs a named owner and a clear risk classification. High-impact agents that can move money, change records, or access sensitive data get the tightest controls.
Step 3: Redesign identity and access for agents.
Give each agent its own identity separate from human accounts. Apply least privilege and zero standing privilege. Privileges are granted for the duration of a task and then revoked. NIST’s agent identity tenets provide a solid checklist here.
Step 4: Insert deterministic policy gates.
Never let the model authorize its own actions. A policy monitor or agent harness evaluates every tool call against written rules before execution. Sandboxes and network isolation keep the blast radius small.
Step 5: Secure the data and model supply chain.
Validate data lineage. Scan for poisoning. Lock down pretrained components and open-source dependencies. Treat model weights and fine-tuning data as high-value intellectual property.
Step 6: Build continuous monitoring and kill switches.
Log every agent action in a tamper-evident store that the agent cannot alter. Maintain the ability to revoke credentials or shut down an agent instantly.
Step 7: Red-team regularly and update the threat model.
Assume the adversary understands your architecture. Test for prompt injection, tool misuse, and multi-agent collusion.
This sequence is deliberately sequential. Skipping inventory or identity work usually creates expensive rework later.
Comparison of Approaches: Bolt-On vs. By Design
| Aspect | Bolt-On Security | Securing AI by Design |
|---|---|---|
| Timing | After deployment or after first incident | From architecture and design stage |
| Privilege model | Shared or overly broad credentials | Distinct agent identities, least privilege |
| Policy enforcement | Often relies on model behavior | Deterministic gates outside the model |
| Visibility | Reactive logs and alerts | Continuous, independent monitoring |
| Change cost | High—retrofits disrupt production | Lower—controls evolve with the system |
| Typical outcome | Frequent exceptions and shadow workarounds | Predictable, auditable operations |
Common Mistakes and How to Fix Them
Securing AI by design for technology leaders The most frequent failure I see is treating AI agents like ordinary service accounts. Shared API keys and long-lived tokens turn a single compromised agent into a lateral-movement machine. Fix: issue short-lived, scoped credentials tied to a unique agent identity.
Another classic: relying on the model’s system prompt as the primary control. Prompts are suggestions, not enforcement. Fix: move authorization logic into deterministic code that the model cannot override.
Shadow AI is still rampant. Teams spin up agents in personal accounts or unapproved SaaS tools. Fix: continuous discovery across cloud environments, code repos, and SaaS platforms, combined with clear policy and easy approved alternatives.
Finally, many organizations stop at monitoring. Logging is necessary but insufficient. You need the ability to stop an agent mid-action. Design for stoppability from the beginning.
Making Securing AI by Design for Technology Leaders Operational
Start with one high-visibility use case. Apply the full set of controls. Measure the time from detection to containment. Use that data to expand the program. Pair the technical work with clear governance—someone has to own the AI risk register and the policy decisions.
Frameworks help. The NIST AI Risk Management Framework gives structure for governance, mapping, measurement, and management. Pair it with threat catalogs such as MITRE ATLAS and the OWASP guidance for LLM and agentic applications. For deeper reading on secure software practices that now cover generative AI, see the NIST Secure Software Development Framework community profile.
CISA’s secure-by-design principles remain relevant: take ownership of security outcomes, practice transparency, and make security a leadership priority rather than a compliance checkbox.
Key Takeaways
- Treat models and agents as untrusted by default.
- Embed security requirements in every design and build phase.
- Give agents distinct identities and least privilege with zero standing rights.
- Keep policy enforcement deterministic and outside the model.
- Maintain continuous discovery, monitoring, and the ability to shut agents down.
- Inventory first—shadow AI is still the largest uncontrolled risk for most organizations.
- Align technical controls with an AI risk management process that leadership actually uses.
- Measure containment speed, not just detection volume.
Securing AI by design for technology leaders Technology leaders who treat securing AI by design as an architecture problem rather than a tooling problem ship faster and sleep better. The next concrete step is straightforward: pick one production agent this week, map its current privileges and data access, and rewrite them under least-privilege rules. Everything else builds from there.
FAQs
What does securing AI by design for technology leaders actually require in practice?
It requires treating security as a first-class design constraint from the architecture stage, assigning unique identities and scoped privileges to agents, enforcing policy outside the model, and maintaining continuous visibility and stoppability.
How is securing AI by design for technology leaders different from traditional application security?
Traditional application security assumes relatively predictable code paths. AI systems introduce probabilistic behavior, tool use, and autonomy, so controls must assume the model itself can be manipulated or misaligned and must limit its authority accordingly.
Where should a technology leader start with securing AI by design?
Begin with a complete inventory of models, agents, and data flows, then redesign identity and access for the highest-risk agents using least privilege and deterministic policy gates.

